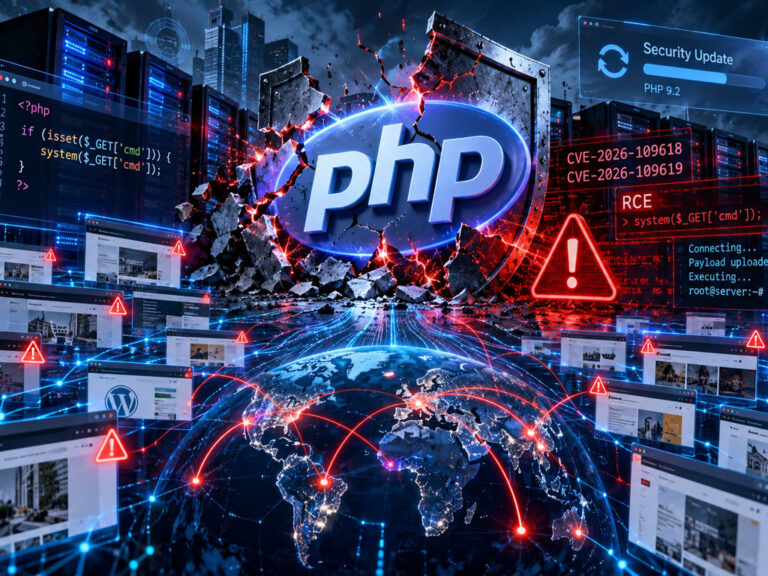
COLOMBO — Website owners and hosting companies worldwide have been urged to install emergency security updates after two critical vulnerabilities were identified in PHP, the programming language underpinning millions of websites and online services, potentially allowing attackers to take control of vulnerable servers without passwords or administrative authorisation.
The PHP development team released security patches on October 21, 2026, following an unprecedented coordinated warning from European cybersecurity authorities.
Both vulnerabilities carry a severity rating of 9.2 out of 10 under the Common Vulnerability Scoring System (CVSS v4.0), placing them in the critical category.
The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, could allow unauthenticated remote code execution, a form of attack in which an external actor runs malicious instructions on an affected computer system.
Successful exploitation could expose sensitive information, compromise website operations or provide attackers with extensive control over servers.
The European Union’s Computer Emergency Response Team (CERT-EU) has advised organisations to apply the fixes urgently and consider isolating vulnerable internet-facing systems when immediate remediation is impossible.
Emergency PHP Security Updates Now Available
The PHP development team initially warned users on October 20 that two critical vulnerabilities had been identified and that emergency fixes would be released the following day.
On October 21, security updates became available for the supported PHP branches.
The patched versions are:
| PHP version | Security update |
|---|---|
| PHP 8.5 | 8.5.12 |
| PHP 8.4 | 8.4.27 |
| PHP 8.3 | 8.3.36 |
| PHP 8.2 | 8.2.35 |
Administrators operating affected versions should upgrade to the appropriate patched release or a newer secure version.
PHP versions 8.1 and earlier are no longer supported by the PHP project’s regular security maintenance programme, making migration to a supported branch particularly important.
The PHP team has warned that the vulnerabilities affect installations serving web requests through configurations including Apache with mod_php, PHP-FPM, php-cgi, LiteSpeed and FrankenPHP.
It identified Apache’s mod_php configuration as presenting especially serious exposure, citing a demonstrated attack that could be triggered before application code executes.
The vulnerabilities are not confined to any single website management system.
WordPress, Drupal and Joomla Among Potentially Affected Platforms
PHP powers widely used content management systems and web applications, including WordPress, Drupal, Joomla and Magento.
The security warning therefore has implications for individual blogs, business websites, online stores, educational institutions and government services.
Cybersecurity company Huntress has highlighted PHP’s extensive use across websites, hosting environments, control panels and applications whose owners may not even realise they depend on the language.
An attacker exploiting a vulnerable PHP installation could potentially interfere with the underlying server rather than merely compromise an individual website plugin or theme.
Depending on the server configuration and the attacker’s access, the consequences could include unauthorised execution of code, exposure of confidential information, disruption of services and further compromise of connected systems.
However, identifying a vulnerability does not mean that every website using PHP has already been hacked.
The actual risk depends on the PHP version installed, its configuration, exposure to the internet and whether the relevant security updates have been applied.
Why Ordinary WordPress Updates May Not Protect Websites
The distinction between PHP and the applications running on it is particularly important for WordPress administrators.
Updating WordPress themes, plugins or the content management system itself does not necessarily update the PHP software installed on the web server.
PHP operates within the hosting environment, and its version is commonly controlled by the hosting provider or server administrator.
WordPress confirmed on October 21 that the two vulnerabilities are not specific to WordPress and that no WordPress software update is required to address them.
Instead, website owners must ensure that their hosting environment uses a patched PHP release.
Administrators can identify their PHP version from the WordPress dashboard by opening:
Tools → Site Health → Info → Server
Many hosting providers also display the active PHP version in their administration panels.
A website that shows its WordPress software and plugins as fully updated may still remain exposed if its underlying PHP installation has not received the emergency fixes.
European Cybersecurity Agencies Issue Coordinated Warning
The seriousness of the vulnerabilities prompted a joint statement involving the European Commission, the European Union Agency for Cybersecurity (ENISA), CERT-EU, Europol’s European Cybercrime Centre and national cybersecurity response teams.
The organisations urged website operators to identify PHP installations, coordinate with hosting providers and immediately deploy the released security updates.
Particular priority was given to internet-facing systems because these can be reached directly through public networks.
CERT-EU advised organisations unable to apply the fixes promptly to consider isolating affected applications from public access until remediation is completed.
The United Kingdom’s National Cyber Security Centre issued similar advice, indicating that temporarily taking vulnerable systems offline may be appropriate where they cannot be protected adequately.
Australia’s Cyber Security Centre also issued a critical alert, warning website operators to identify vulnerable PHP environments, review official security guidance and monitor systems for suspicious activity.
The Australian advisory initially noted that versions dating back to PHP 5 could potentially be affected, although operators should consult the latest official guidance for the precise supported and fixed releases.
What Website Owners Should Do Immediately
Cybersecurity authorities and PHP developers have recommended several measures to reduce exposure.
1. Contact Your Hosting Provider
Website owners should establish which PHP version their website is running and confirm whether the hosting provider has installed the October 21 security updates.
Where hosting is managed by a third party, administrators should seek confirmation that the relevant PHP runtime has been patched rather than assuming that routine WordPress updates are sufficient.
2. Install the Correct Security Update
Administrators responsible for their own servers should upgrade to the appropriate patched PHP version as soon as possible.
Before making changes to production systems, they should ensure that current backups are available and check application compatibility.
Older PHP branches should be replaced with supported versions wherever possible.
3. Review Temporary Security Measures
Web application firewalls and services such as Cloudflare may help filter suspicious requests or reduce exposure to some attacks.
However, the PHP development team has warned that no complete alternative mitigation is available.
Firewall protection should therefore be treated as an additional security measure rather than a substitute for installing the official patches.
Where critical vulnerabilities cannot be remediated promptly, temporarily restricting public access or isolating the affected server may be necessary.
4. Monitor Systems for Suspicious Activity
Administrators should review server logs, application errors and unusual access patterns.
Warning signs can include repeated PHP memory errors, unexpected server crashes, unfamiliar files, suspicious processes and attempts to access sensitive resources.
If a server may already have been compromised, installing the patch alone may not remove malicious software or unauthorised changes introduced earlier.
Professional incident-response assistance may be necessary.
Why the Threat Matters to Sri Lankan Websites
Sri Lankan businesses, media organisations, government agencies, educational institutions and online retailers also depend on PHP-based systems.
Many websites operate through shared hosting services, where customers have limited control over server software.
This makes coordination with hosting providers essential.
A compromised website can affect more than the information displayed to visitors. Online services may store customer records, account credentials, transaction information and confidential business material.
For news organisations, an attack could interfere with publishing operations, alter website content or interrupt access to information.
Businesses relying on digital services could face operational disruption and reputational damage.
However, there is no basis for concluding that a specific Sri Lankan website has been compromised merely because it uses PHP.
Website owners should confirm their exposure through technical checks rather than assumptions.
Security Patching Must Take Priority
The discovery of these vulnerabilities illustrates the importance of maintaining the underlying technology on which modern websites operate.
Routine application updates are necessary but insufficient when the security weakness exists within the server’s programming environment.
PHP’s emergency security releases provide a direct remedy for supported versions, while older installations require particular attention because they may no longer receive official maintenance.
For website administrators, the immediate priorities are clear: identify the installed PHP version, apply the appropriate security update, verify that the change has taken effect and examine systems for any signs of compromise.
Organisations unable to patch vulnerable public-facing systems promptly should assess whether access must be restricted until the risk can be addressed.
With fixes now available, the most consequential question is no longer when the PHP developers will respond, but how quickly website operators and hosting companies can secure the systems under their control.