By Marlon Dale Ferreira
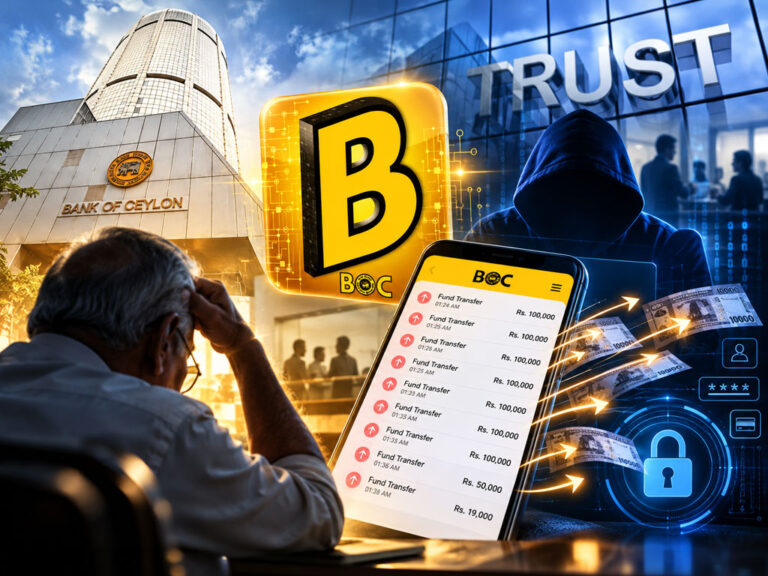
Bank of Ceylon customer trust faces scrutiny after a family disputed Rs. 2.869 million in transactions completed within just 14 minutes.
There was a time when withdrawing even a small amount of money from a bank was a deliberate exercise. There were no ATMs dispensing cash within seconds, no plastic cards tucked into wallets and no banking apps placing an entire account behind a mobile phone screen.
A customer would fill out a withdrawal slip in blue ink, sign it and approach the counter with a national identity card and bank passbook.
The process was slow, sometimes painfully so. Yet behind that process was something modern banking risks taking for granted: a human relationship built on trust.
Many bank counters once displayed a familiar passage commonly attributed to Mahatma Gandhi:
“A customer is the most important visitor on our premises. He is not dependent on us. We are dependent on him.”
The sentiment continues by describing the customer not as an interruption to business, but as its purpose.
There is, however, an important historical qualification. Although the quotation has been attributed to Gandhi for decades, the Mani Bhavan Gandhi museum notes that no source for it exists anywhere in the 100 volumes of Gandhi’s collected works. Research into its origins has traced substantially similar wording to business literature from the early 1940s.
Its authorship may be uncertain. Its principle is not.
The customer is the reason a bank exists.
From the Bank Counter to the Algorithm
Banking has changed almost beyond recognition. Digitalisation has made transactions faster, more convenient and available around the clock.
That progress has enormous value. But efficiency cannot be allowed to create distance between financial institutions and the people whose money they hold.
Technology changes how a bank serves its customers. It does not remove the bank’s responsibility to serve them.
The Central Bank of Sri Lanka has established a regulatory framework for financial consumer protection, covering areas such as transparency, responsible business conduct, protection of consumer assets and information, and complaint handling.
Rules, however, matter most when customers discover whether they work at the moment something goes wrong.
That question has become particularly relevant following the disputed transactions involving a retired Sri Lanka Army nursing officer and his Bank of Ceylon account.
Midnight, 30 Transactions, and One Helpless Family
Bank of Ceylon transactions totaling Rs. 2.869 million are disputed by a customer, while BOC says its systems suffered no security breach.
Read MoreRs. 2.869 Million in 14 Minutes
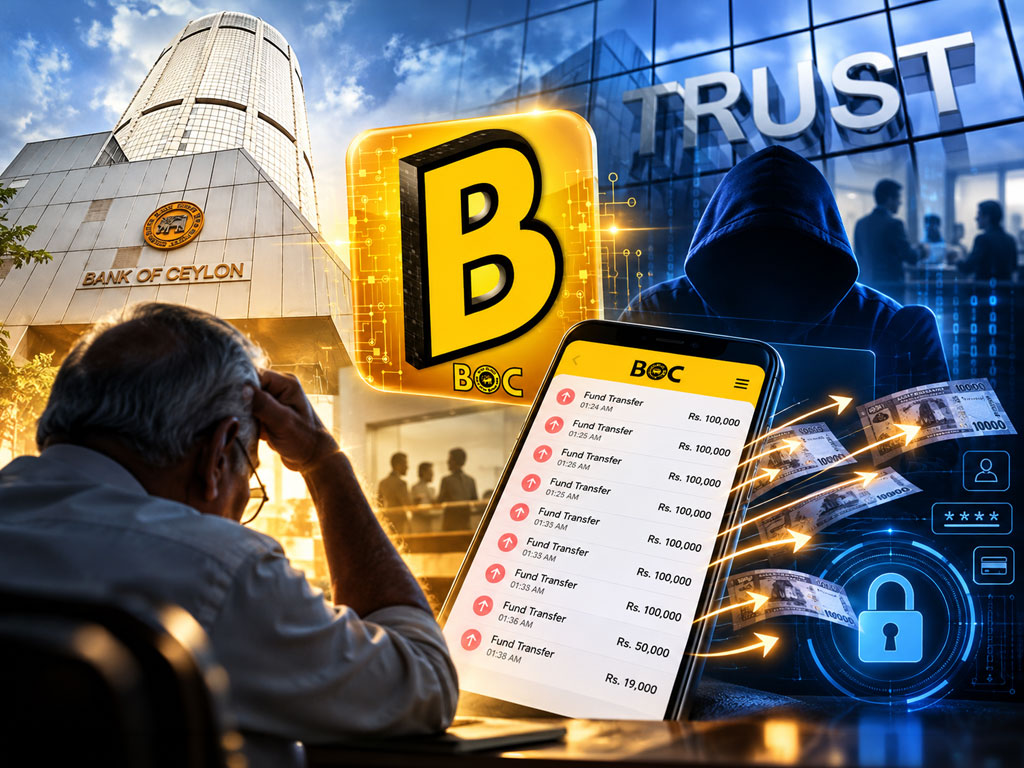
On August 14, according to the account holder’s family, Rs. 2,869,000 was transferred from his BOC account in 30 transactions between 1.24 a.m. and 1.38 a.m.
Twenty-eight transfers were for Rs. 100,000 each. Two further transfers of Rs. 50,000 and Rs. 19,000 brought the disputed total to Rs. 2.869 million.
The family says the money formed part of a Rs. 4.4 million loan obtained by pledging the retired nursing officer’s pension, with the funds intended to help them build a permanent home.
They maintain that the transactions were unauthorised.
According to the family, repeated SMS notifications alerted them to the transfers and they contacted the BOC hotline seeking to have the account and card blocked. They allege that the transfers nevertheless continued.
For a family watching its borrowed money disappear, 14 minutes is not the triumph of digital efficiency. It is an eternity.
Yet this is precisely where commentary must be separated from established fact.
The Morning Telegraph has not independently established how the transactions were authorised, whether the customer’s credentials were compromised, or precisely what occurred between the customer contacting the hotline and the final transfer being completed.
Those are questions for the continuing investigation.
BOC Says Its Systems Were Not Breached
Bank of Ceylon has rejected suggestions that the incident resulted from a failure or security breach within its systems.
In its response, the bank said the disputed transactions had been authenticated using the customer’s internet banking login credentials and One-Time Passwords, or OTPs. BOC maintained that its investigation found no security breach, unauthorised access or technical fault in its digital banking infrastructure.
That position matters.
It means the dispute cannot responsibly be reduced to the assertion that Rs. 2.869 million simply “vanished” because BOC’s technology failed. The customer disputes the transactions; the bank says they were authenticated through the required credentials.
Those two positions now require proper investigation.
But even if a bank’s underlying system has not been breached, another question remains relevant to the future of digital banking: what should happen when a customer’s account suddenly begins making a sequence of unusual transactions?
Twenty-eight consecutive transfers of Rs. 100,000, followed by another two transfers, within 14 minutes shortly after midnight inevitably invite questions about fraud detection, transaction monitoring and the speed with which a financial institution can respond to a customer’s emergency call.
That is not the same as concluding that BOC was legally or technically responsible for these disputed transactions. The available evidence does not establish that.
It is a question about what customers should reasonably expect from modern banking.
Technology Should Strengthen Trust, Not Replace It
Banks now operate sophisticated digital systems capable of authenticating customers, processing transactions within seconds and analysing enormous quantities of financial information.
As banking becomes more automated, customers may reasonably expect security mechanisms to become more sophisticated as well.
An OTP can help establish that a transaction passed through a particular authentication process. But in an age of phishing, social engineering, credential theft and increasingly sophisticated digital fraud, authentication is only one part of the wider security challenge.
Financial institutions must continually examine whether transaction-monitoring systems can identify behaviour that differs sharply from a customer’s normal pattern and whether intervention can occur quickly enough when the customer reports suspected fraud.
That is a policy question extending far beyond one BOC account.
The original complaint also raises an intensely human question.
What happens when a customer calls a bank while watching money leave an account?
Can the hotline immediately suspend digital access? Can pending transactions be interrupted? How quickly can a suspected recipient account be flagged? When must another financial institution be contacted? What information should the customer receive while an investigation is underway?
Customers should know the answers before they become victims of suspected fraud, not afterwards.
Responsibility Cannot End With a Password
The temptation in digital banking is to reduce every dispute to authentication.
Was the password correct?
Was the OTP entered?
Were the credentials valid?
Those are crucial technical questions. They are not necessarily the only questions.
A financial institution’s responsibility in the digital age also includes designing systems that anticipate the reality that customers can be deceived, manipulated or compromised.
At the same time, customers have responsibilities of their own. Passwords, PINs and OTPs must be protected. Suspicious messages and links should be treated cautiously, and suspected compromise should be reported immediately.
Consumer protection cannot function effectively if either side treats cybersecurity as exclusively the other’s responsibility.
That is why the BOC case deserves a thorough investigation rather than an instant verdict.
If the bank’s systems functioned exactly as designed, that should be established.
If the customer’s credentials were compromised, investigators should determine how.
If there were opportunities to detect or interrupt the disputed transactions, those should also be examined.
And if improvements can prevent another customer from experiencing the same ordeal, they should be implemented.
Trust Is Still the Bank’s Greatest Asset
State banks occupy a distinctive place in Sri Lankan society.
Generations of families have entrusted their salaries, pensions, savings and borrowings to institutions such as the Bank of Ceylon. For many customers, that relationship is not simply commercial. It is built over decades.
Digitalisation should strengthen that trust rather than make customers feel abandoned when technology fails them or when they believe they have become victims of fraud.
The old customer-service quotation displayed behind bank counters may have been misattributed to Gandhi, but its underlying message remains relevant.
Customers are not an inconvenience standing between a bank and greater efficiency. They are the reason the institution exists.
The challenge for modern banking is to carry that principle beyond the counter, into mobile applications, call centres, fraud-monitoring systems and boardrooms.
The final outcome of the Rs. 2.869 million dispute remains to be established. Until investigators determine what happened, neither the customer’s allegation nor the bank’s explanation should be treated as the final word.
But one lesson does not need to wait for that outcome.
A bank can digitise almost everything.
Trust is harder to automate.